So, you’re diving into AWS and DNS stuff, huh? Exciting times! Seriously, it can feel like a rollercoaster ride.
You’ve probably got a million questions swirling around in your head. Like, how do I set this up? What’s the best way to handle DNS?
Look, configuring DNS in AWS isn’t as scary as it seems. You just need a few tips and tricks up your sleeve to make things smoother.
In this chat, we’re gonna break down some best practices that’ll make you feel like a pro. You’ll be zipping through configurations before you know it!
So grab a snack and let’s get into the nitty-gritty of AWS DNS!
Understanding AWS Public DNS Server: Legal Considerations and Compliance
Maximizing Performance and Reliability with AWS Public DNS Server
To understand AWS Public DNS server and its legal considerations, you first need to grasp what a DNS (Domain Name System) is. Basically, it’s like the phonebook of the internet. When you want to visit a website, the DNS translates the web address into an IP address that your computer can understand.
Now, when it comes to AWS (Amazon Web Services), their Public DNS servers work similarly. They handle the translation of domain names for customers using AWS services. But this brings up some **legal considerations**:
Compliance with Data Regulations: You know, different regions have varying laws about data privacy. For example, if you’re operating in Europe, you’ll need to comply with GDPR (General Data Protection Regulation). AWS provides various compliance frameworks that can help you stay within these legal boundaries.
Data Sovereignty Issues: Depending on where your data is physically stored and handled can affect your compliance obligations. Using AWS services means understanding where your data resides and ensuring it adheres to local laws.
Accountability for Action: If there’s a service outage or another issue—hey, it happens—you might need to show that you followed best practices in managing your DNS settings. Document everything! This way, if something goes wrong legally or technically, you’ve got proof that you did everything right.
So yeah, having an understanding of these legal aspects is crucial when using AWS Public DNS.
Now let’s talk about maximizing performance and reliability with AWS Public DNS servers:
Reduce Latency: The closer your server is to your end-users, the faster the response times will be. When properly configured, AWS’s global infrastructure can minimize latency significantly.
Use Caching Effectively: Caching helps reduce load times by storing frequently accessed data temporarily. For instance, if several users request the same information frequently, caching allows them faster access instead of going through full resolution each time.
Health Checks and Failover: Setting up DNS failover ensures that if one server goes down—let’s say there’s an unexpected outage—traffic automatically reroutes to another healthy server. This keeps services running smoothly while minimizing downtime.
In summary: using AWS Public DNS servers isn’t just about getting traffic routed quickly; it’s also about being mindful of legal stuff while maximizing how well everything works!
Comprehensive Guide to AWS Route 53 Documentation for Effective DNS Management
AWS Route 53 is a powerful tool for managing DNS (Domain Name System) effectively. If you’re looking to understand how to handle DNS configuration with it, you’ve come to the right place. Let’s break down the essentials.
What is Route 53? Well, it’s Amazon’s cloud-based DNS web service. What that means is you can route internet traffic to your resources, like websites or applications, using simple configuration steps.
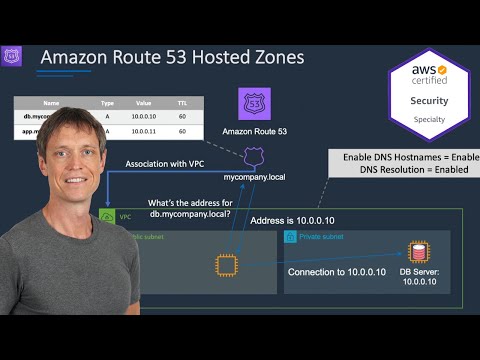
First things first, when you start with Route 53, you need to create a hosted zone. This is like a container for your DNS records. Each domain has its hosted zone where all of that domain’s settings live.
Types of Records: You’ll mainly work with different types of records within this hosted zone:
Understanding these records is crucial; it’s like knowing the different types of signs you might see on a road. They all serve different purposes!
Create and Manage Records: To add a record, you can simply go into your hosted zone and click «Create record.» Fill in details like the record type and value. It’s pretty straightforward! One time I got mixed up between A and CNAME records while setting up my site—it threw off my domain for hours until I realized it! Lesson learned: always double-check.
Also, do not overlook TTL (Time To Live). This setting tells servers how long they should cache your DNS information. A lower TTL means changes propagate faster but might result in increased queries on your end.
Now let’s chat about DDoS protection. Amazon Route 53 integrates well with AWS Shield for additional security against Distributed Denial of Service attacks. You wouldn’t want a sudden surge of malicious traffic taking down your site when all was good just moments before!
Health ChecksThis can lead to issues later!, so take time upfront for organization. Using tags and defining naming conventions helps keep everything clear.
Lastly, always keep an eye on AWS documentation. It will be updated regularly with best practices and new features that can optimize how you manage DNS using Route 53.
So there you have it! Understanding AWS Route 53 might seem overwhelming at first glance, but breaking it down makes it easier—just like piecing together a jigsaw puzzle slowly but surely finding that picture in the end!
Understanding AWS Public DNS Resolver: Enhancing Network Security and Performance
Understanding AWS Public DNS Resolver can really make a difference in how your network operates. It’s all about improving both security and performance, you know? You might be asking yourself, “What exactly is a DNS Resolver?” Well, it’s basically like the phone book of the internet. When you type a website name into your browser, the DNS translates that into an IP address so your computer can find it. But AWS takes it a step further.
With AWS Public DNS Resolver, you’re not just getting any old resolver. This service helps route your queries efficiently and securely. Imagine visiting your favorite sites without worrying too much about security risks like DDoS attacks or phishing attempts—sounds nice, right?
Another cool thing is that it can help enhance network performance. It often uses intelligent routing to direct traffic to the nearest endpoint available. Think of it this way: when you request a webpage, AWS will try to connect you through the quickest path possible. This makes loading times faster; who doesn’t want that?
It also keeps things secure by leveraging features like DNS Security Extensions (DNSSEC). This verifies if the responses you’re getting from DNS queries are legit and haven’t been tampered with. So essentially, it adds that extra layer of trust to what you’d be accessing.
Now, let’s look at some key benefits:
- Improved Performance: Quick response times mean better user experience.
- Security Enhancements: Prevents certain types of cyber threats.
- Simplified Management: Easy configuration through the AWS Management Console.
- Scalability: Adjusts based on traffic needs without physical limitations.
When setting up this service, many folks overlook best practices in DNS configuration which can mess things up later on. For instance, using multiple Availability Zones ensures higher reliability—if one goes down, others are still there to keep things running smoothly.
And just as an added note: remember to monitor your DNS queries and performance metrics regularly. You don’t wanna be in the dark about any potential hiccups affecting users’ access or security.
In wrapping this up, using AWS Public DNS Resolver has its perks in boosting both security and overall network performance. Plus, sticking with best practices for configuration means you’re already setting yourself up for success!
So, let’s talk about AWS DNS configuration, yeah? It can feel a bit overwhelming at first. I remember the first time I had to set it up for a project. My mind went blank! I knew it was important but didn’t quite know where to start.
When you dive into AWS and begin messing with Route 53, you quickly realize how crucial DNS is for your services. It’s like the internet’s phone book; without it, no one can find your website or applications. If you don’t get this right, it could lead to all sorts of frustrating moments—like when you’re trying to access your site and it just won’t load.
One of the key things that pops up a lot when you’re setting up AWS DNS is planning. You really need to think about how you want your domain structured ahead of time. Should you have multiple subdomains? What about health checks? And then there’s latency; nobody wants their site taking ages to load.
Then there are best practices like using weighted routing policies or failover configurations that really come in handy. These allow for better traffic management and ensure users get directed to the healthiest resources available, which is super important during traffic spikes.
Security is another biggie—managing access permissions carefully is vital so that unauthorized changes don’t slip in unnoticed. At my last gig, we had an incident where a small misconfiguration led to downtime. Talk about a panic moment!
And let’s not forget regular monitoring and logging with CloudWatch! Keeping an eye on how your DNS records perform gives insight into what needs tweaking here and there.
So, while it might seem daunting at first glance, once you wrap your head around these practices and create a solid foundation for your DNS setup in AWS, everything gets easier from there on out! Seriously though; embracing this aspect makes managing any online service way less stressful in the long run. Just take it step by step—you got this!
