So, you’ve heard about web application firewalls, right? They sound kind of techy and maybe a bit intimidating. But hang on a sec; they’re super important if you’re in the online game.
You know that feeling when you hit “send” on an email or upload something online, and you just hope it gets to where it needs to go without a hitch? That’s kind of like what your data goes through. Enter the web application firewall, or WAF for short.
It’s like a security guard for your website. But instead of standing at the door with a clipboard, it’s sitting in the digital realm making sure everything’s safe and sound.
In this little dive, we’ll break down exactly what learning mode is and why it matters for your site. So whether you’re running a blog or an e-commerce powerhouse, stick around! It’s going to be fun, I promise!
Understanding Web Application Firewalls: Key Examples and Best Practices
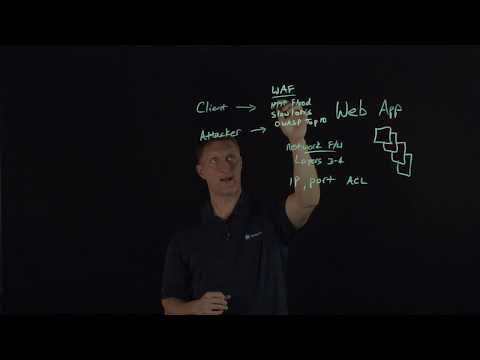
Web Application Firewalls (WAFs) are like the security guards of your favorite websites and online apps. They sit between the user and the web server, making sure that only legitimate traffic gets through. When you send a request, the WAF checks it for any malicious activity. If something looks fishy, it can block that request. Pretty cool, right?
So, what exactly do they protect against? Well, here are some key points:
- SQL Injection: This is when someone tries to send harmful SQL commands through a web app to manipulate databases.
- Cross-Site Scripting (XSS): Attackers inject malicious scripts into web pages viewed by users. This can lead to stolen data or session hijacking.
- Cross-Site Request Forgery (CSRF): This tricks users into performing actions they didn’t intend to on a different site.
These attacks can cause serious harm to businesses and users alike! I remember one time when a small online store I used got hit hard by an XSS attack. My info got lifted right off their site! They managed to fix things after but it was super stressful.
When using a WAF, you’ve got two main types: network-based and cloud-based.
Network-based WAFs sit on your premises and offer low latency since they’re closer to your servers. But they can be pricey and take some serious setup time. On the other hand, cloud-based WAFs don’t require as much maintenance and can be scaled easily based on traffic demands.
Now let’s talk about best practices to get the most out of your WAF:
- Regular Updates: Keep the firewall rules fresh! Cyber threats evolve fast; you gotta stay ahead.
- Tuning and Testing: Continuous monitoring ensures that your WAF is working as it should—like tuning up a car!
- User Education: Make sure everyone knows how to use the web apps securely; sometimes humans are the weak link.
If you follow these practices, you’ll have fewer headaches down the line.
Also, it’s worth mentioning that while WAFs are crucial for protection, they shouldn’t be your only line of defense. Think of them like wearing shoes while running outside; they’re essential but not all you need!
In summary, Web Application Firewalls play an important role in securing online environments against common threats. With careful selection and proper management—plus those best practices—you’ll add an extra layer of safety for everyone involved. Seriously, staying safe online should never feel like an afterthought!
Comprehensive Guide to Web Application Firewalls: Enhancing Security for Your Online Applications
Web Application Firewalls, or WAFs for short, are a big deal these days in keeping your online applications safe. Basically, they act like a shield between your web application and the internet—blocking attacks before they even reach you. Let’s break it down simply.
What is a WAF?
A Web Application Firewall monitors and filters incoming HTTP requests to your web applications. It scans for malicious data or patterns that could exploit vulnerabilities. If you think of your web app like a house, the WAF is like the security guard at the front gate checking who’s coming in.
How Does it Work?
WAFs analyze traffic based on predefined security rules. This means they can look for things like SQL injection attempts or cross-site scripting (XSS). When they spot something suspicious, they can either block it or alert you right away.
Types of WAFs
There are two main types of WAFs: network-based and cloud-based.
- Network-based WAFs: These are usually hardware solutions installed on-premises. They tend to be faster since they’re closer to the application.
- Cloud-based WAFs: These are managed by service providers and can be set up quickly with no hardware involved. They also offer scalability, which is super helpful if you’re growing.
Key Benefits
Implementing a WAF has multiple upsides:
- Protection Against Attacks: A good WAF can defend against various attacks, including DDoS (Distributed Denial-of-Service) and data theft.
- Easier Compliance: It helps with compliance regulations like PCI-DSS, HIPAA, etc., which often require certain security protocols.
- Improved Performance: Some advanced WAFs even optimize traffic flow by caching frequently-requested content.
You might wonder about tuning a WAF. Well, this involves adjusting the rules to suit your specific application needs. Too strict? You might block legitimate users. Too lenient? You leave yourself exposed! It’s kind of a balancing act.
Also, keep in mind that while a WAF provides excellent protection, it shouldn’t be your only defense layer. Think of it as part of a comprehensive security strategy that includes firewalls at different levels and regular vulnerability assessments.
The Importance of Learning Mode
A lot of modern WAFs come with **Learning Mode**, which allows them to analyze normal traffic patterns over time before enforcing strict rules. This way, when they see something unusual—that could mean trouble—they know how to react appropriately without blocking legitimate users mistakenly.
In essence, incorporating a Web Application Firewall into your security stack offers robust protection for your valuable online assets while providing flexibility to adapt as threats evolve. So if you’re running an online app—seriously consider looking into this crucial layer of defense!
Master Web Application Firewall: Comprehensive Course for Enhanced Online Security
Web Application Firewalls, or WAFs, are like security guards for your website. They sit between your web app and the internet, watching all the traffic going in and out. When you think about it, it’s pretty crucial to have that layer of protection, right? Bad actors online are constantly trying to exploit vulnerabilities, and that’s where a WAF steps in.
Understanding Learning Mode is key. It’s basically a feature that allows the WAF to get smarter over time. In this mode, the firewall observes your web application’s traffic patterns to learn what normal behavior looks like. By doing this, it can better identify suspicious activities later on. Think of it as training wheels—you gain confidence as you understand how things work.
When you’re setting up this mode, you’re looking at a couple of different features:
But here’s where it gets interesting: after it finishes its learning phase, the firewall uses those insights to block any malicious requests more effectively. You obviously want your app running smoothly while keeping pests out.
Also important is Tuning. Once you’re done with learning mode, you’ll likely need to adjust some rules based on the data collected. For instance, if legitimate users often trigger false alarms because they’re entering data in a way that’s seen as suspicious—like lots of special characters—you can tweak those settings.
You could end up blocking harmless users instead of actual threats! Not cool, right? As you tune these rules over time based on user feedback and ongoing analysis, your WAF becomes even more effective at keeping bad stuff out while letting good traffic flow freely.
In summary, understanding how Learning Mode works with a Web Application Firewall can really boost your online security game. You get that proactive approach rather than just reacting after an attack has occurred. That kind of foresight makes all the difference when you’re trying to keep your web application safe from cybercriminals lurking in cyberspace.
So, learning modes can really be super helpful when it comes to web application firewalls (WAFs). You might be wondering, what’s a WAF anyway? Well, think of it as a security guard for your website. Just like that buddy who’s always watching out for you when you’re out there in the world, a WAF monitors and filters incoming traffic to protect your web applications from various online threats. Pretty neat, huh?
Now, here’s where learning mode kicks in. It’s like this training phase where the WAF studies normal traffic patterns. Imagine your friend watching how you usually go about your day—where you hang out, who you talk to—so they can spot anything unusual later on. The WAF gathers this data and builds a profile of what “normal” looks like for your site.
The neat part is that with the learning mode activated, the WAF doesn’t just block traffic immediately; it analyzes requests and learns from them first. So if something looks slightly off—like maybe someone trying to access areas they shouldn’t—it can take notes instead of just freaking out and shutting everything down. This way, once it moves into active blocking mode, it’s smarter about what gets through.
I remember when I first set up a web application for a small project I was working on. It was such a hassle dealing with all those annoying spam bots trying to mess things up! I stumbled upon a WAF with a learning mode feature and decided to give it a shot. Honestly? It felt like I had an extra pair of eyes on my project—less stress knowing that something was out there keeping an eye on things while I focused on the fun parts of building my app.
However, there are some things to keep in mind! Learning modes can take time; they need to collect enough data to differentiate between normal and malicious activity effectively. If you’re in a fast-changing environment (like running an online store during sales season), you might want to be cautious about relying solely on this feature.
And don’t forget: while learning modes help improve security over time, they’re not bulletproof! You still need other layers of protection because cyber threats are constantly evolving.
So yeah, diving into learning modes for web application firewalls is like setting up a little surveillance system that gets better at spotting trouble without being too jumpy right away. In short? It gives your apps some smart backup against the digital bad guys!
