So, you’ve got a Lighttpd server up and running? Nice! That’s like having a little slice of the internet all to yourself. But, here’s the thing: it needs some love to keep those nasty hackers at bay.
Seriously, the web can be a wild place. You never know who’s lurking around, waiting to take advantage of a weak spot. It’s like that moment when you forget to lock your front door at night—yikes!
Don’t worry though, securing your server doesn’t have to be rocket science. I mean, we’re just trying to make sure your online home is safe and sound. So let’s chat about some simple best practices that’ll help you sleep easier at night. Ready? Let’s roll!
Best Practices for Securing Your lighttpd Server: Insights from Reddit Discussions
When you’re running a Lighttpd server, securing it is super important. You don’t want to leave the door wide open for hackers or anyone else with bad intentions. Based on insights from Reddit discussions, here are some solid practices to keep your server safe.
Update Regularly: Keeping your server software updated is crucial. Every new version comes with patches that fix vulnerabilities. Don’t be that person who’s running outdated software because it feels “safer”. Just a quick command can often do the trick.
Use Strong Passwords: You’d be surprised how many people use “123456” or “password” as their login credentials. Using strong and unique passwords for all accounts is key! Think of something complex—mix letters, numbers, and special characters. It’s a pain to remember but worth it.
Disable Unused Modules: Lighttpd allows you to enable or disable modules based on your needs. If there are modules you’re not using, get rid of them! Each active module can be an entry point for attackers. Less is definitely more in this case.
Implement Firewalls: A good firewall can act as your first line of defense against attacks. You want one that filters traffic effectively and blocks suspicious activity. Tools like UFW or iptables can help set this up.
Secure Your Configuration Files: Configuration files often contain sensitive information about your server setup. Make sure they’re not easily accessible and are correctly permissioned so only authorized users can view or edit them.
SSL Certificates: Implementing SSL/TLS encrypts data between the server and clients, which prevents eavesdropping on sensitive information like passwords. It’s a small step that makes a huge difference—plus, Google loves it for SEO!
Regular Backups: Seriously, back up your data! Just imagine losing everything due to a hack or a simple mistake—it feels awful! Automated backups at regular intervals can save you from sleepless nights.
Monitor Logs: Keep an eye on your access logs and error logs regularly. They can reveal suspicious activities that might indicate an attempt to breach the server’s security. Remember: early detection is vital!
So yeah, these practices may feel like a lot at first, but implementing them gradually will significantly improve your Lighttpd server’s security posture. If you follow these steps consistently, you’ll reduce risks and ensure smoother sailing down the road!
Best Practices for Securing Your Lighttpd Server with Pi-hole Integration
When it comes to securing your Lighttpd server, especially when integrating with Pi-hole, you want to keep things tight and safe. You probably don’t want any unwanted guests sneaking into your setup, right? Here are some best practices that can help you fortify your server.
1. Keep Everything Updated
First things first, always keep Lighttpd and Pi-hole updated. This means checking for new versions regularly. Updates often include security patches that fix vulnerabilities. It’s really easy to do; just run a simple command in your terminal.
2. Configure Your Firewall
So, firewalls are like the bouncers of the internet—they control who gets in and who stays out. Make sure to configure your firewall properly by allowing only necessary ports like 80 for HTTP and 443 for HTTPS. You might also want to block other ports that aren’t needed.
3. Use HTTPS
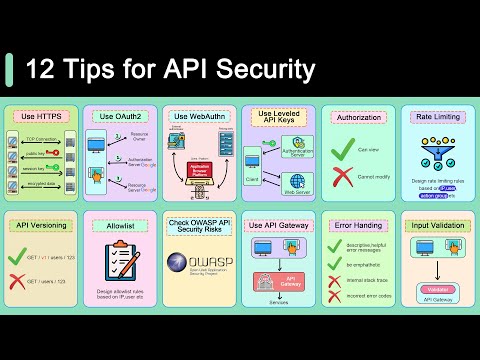
If you haven’t done this yet, you need to switch from HTTP to HTTPS using a service like Let’s Encrypt. It encrypts the data between the server and the client, so even if someone intercepts it, they won’t be able to read it.
4. Secure Your Configuration Files
Check your Lighttpd configuration files for any unnecessary options or modules that could expose vulnerabilities. For example, disable any directory listing features unless absolutely necessary.
5. Use Strong Passwords
This one might seem obvious, but make sure you’re using strong passwords for accessing both Lighttpd and Pi-hole interfaces. Think of long phrases or a combination of letters and numbers—something hard to guess!
6. Enable Access Control
Consider using access control lists (ACLs) in Lighttpd to restrict access based on IP addresses or networks that should have permissions to connect.
7. Monitor Logs Regularly
Regularly check your server logs for unusual activity or signs of unauthorized access attempts. This is actually one of the simplest yet most effective ways to catch issues early on.
8. Back Up Your Data
Don’t forget backups! Regularly back up both your Lighttpd configurations and Pi-hole data so that you can restore everything if something goes wrong.
By following these practices, you’ll be setting up a solid defense around your Lighttpd server integrated with Pi-hole, ensuring it runs smoothly while keeping pesky threats at bay! Always remember: a little prevention goes a long way when it comes to security!
So, you’ve set up a Lighttpd server, huh? That’s pretty cool! Now, the next big thing is keeping it secure. You know, I remember when I first started with web servers. I was just so excited to get everything running that I kinda overlooked security at first. It wasn’t long before I realized how important it was. So, let’s talk about some practices that can really help you keep your Lighttpd server safe.
First off, let’s tackle the basics. Always keep your software updated. It seems simple enough, but you’d be amazed at how many people forget this step. Software developers release patches and updates not just for fun—they’re fixing vulnerabilities! So make sure you’re regularly checking for updates.
Next up is configuring your settings properly. Seriously, pay attention to those config files! You want to lock down access as much as possible. For instance, if you don’t need certain modules, disable them. It’s like cleaning up a messy room; the less cluttered it is, the easier it is to find stuff and spot any problems.
Then there’s HTTPS—definitely worth mentioning. Serving content over HTTPS isn’t just for e-commerce sites or places where personal data is exchanged anymore; it should be standard practice now! Let me tell ya, using HTTPS encrypts the data sent between your users and your server which makes it much tougher for attackers to sniff around.
And hey, don’t forget about user permissions and firewalls! Set up strict user permissions and only give people access to what they absolutely need—kind of like having different keys for different doors in your house. And a good firewall can act as your first line of defense against intruders trying to poke around.
Oh, and one more thing: log monitoring! Keeping an eye on your logs can help you catch suspicious activity early on. When my own server got attacked once (long story!), it was my logging setup that alerted me before things got out of hand.
So yeah, looking after security might feel like a chore sometimes, but it’s super important in keeping everything running smoothly—especially if you’ve worked hard to get it all set up in the first place! It’s all about being proactive rather than reactive. Stay safe out there!
